
Quick Listen:
Updating a medical office phone system is a major operational decision. For practice managers and healthcare administrators, the right upgrade can support clearer communication workflows, easier maintenance, and better alignment with privacy requirements. The process is not only about replacing hardware or choosing a new provider. It requires reviewing how calls move through the practice, how staff handle communication tasks, and what safeguards are needed when technology supports patient interactions.
A thoughtful medical office phone system upgrade starts with understanding current challenges, evaluating future needs, and choosing a solution that fits daily workflows. Practices should consider call routing, after-hours communication, security expectations, staff adoption, and long-term management before making a change.
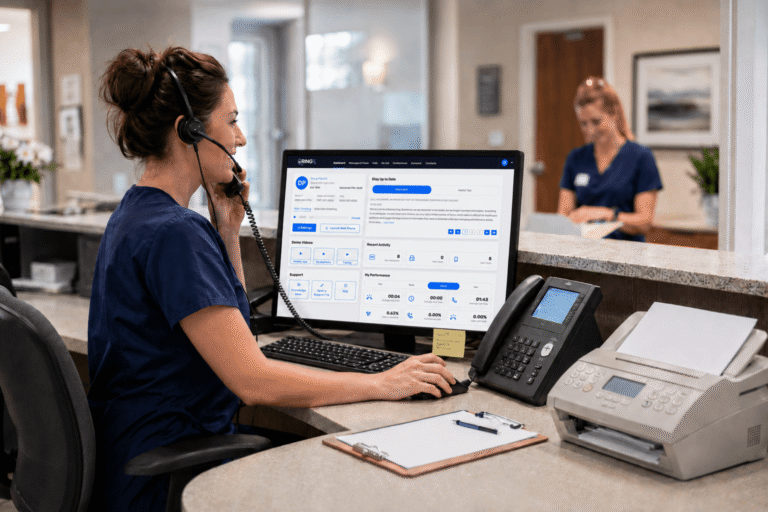
Missed calls, scattered text messages, and voicemails buried in separate apps can slow patient communication and add compliance risk. RingRx brings voice, secure texting, fax, video, and on-call communication into one HIPAA-compliant platform built for healthcare workflows. Start your RingRx free trial today.
Why Should a Medical Practice Review Its Phone System Before Upgrading?
A phone system often becomes part of nearly every patient communication workflow, from appointment inquiries and referrals to voicemail messages and follow-up calls. When a system no longer supports how a practice operates, small issues can create unnecessary administrative work.
Before selecting a replacement, practice leaders should document how communication currently works. This creates a clearer picture of what needs to improve and prevents choosing technology based only on features.
- Review daily call patterns: Identify when call volume increases, which teams handle specific requests, and where handoffs occur.
- Identify workflow gaps: Look for issues such as unclear call ownership, inconsistent voicemail management, or difficult after-hours processes.
- Understand staff needs: Gather input from front-desk teams, clinical staff, and administrators who use the system every day.
- Consider future operations: Evaluate whether the system can support changes in staffing, locations, or communication processes.
The goal is not simply to replace an older phone system. The goal is to create a communication setup that matches the way the practice works today.
What Should Practices Evaluate When Replacing a Medical Office Phone System?
Replacing a medical office phone system requires evaluating more than call quality. Healthcare organizations need to consider how communication tools fit into operational routines, privacy practices, and staff responsibilities.
- Call routing: Review whether calls reach the appropriate person or department without unnecessary transfers.
- After-hours workflows: Understand how urgent and non-urgent calls are handled outside regular office hours.
- Voicemail management: Consider how messages are created, accessed, and followed up on by authorized staff.
- Fax and communication workflows: Review how phone-related tasks connect with other administrative processes.
- Administration: Evaluate how easily office leaders can manage settings, users, and communication rules.
A replacement project should focus on practical workflow improvements rather than selecting the longest feature list. The most useful system is the one that helps teams manage communication consistently.
How Does HIPAA Affect a Phone System Upgrade Decision?
Healthcare communication technology should be evaluated with HIPAA requirements in mind. A phone system does not make a practice compliant by itself, but technology choices can support HIPAA-compliant workflows when combined with appropriate policies, staff practices, and security controls.
- Access controls: Determine how users access communication tools and whether permissions align with staff responsibilities.
- Vendor agreements: Review whether appropriate agreements, such as a Business Associate Agreement when applicable, are available.
- Data handling: Understand how communication information is stored, accessed, and managed.
- Staff procedures: Confirm that employees understand appropriate communication practices, including avoiding unnecessary sensitive information in messages.
Healthcare organizations should also avoid assuming that a new technology automatically solves compliance responsibilities. A secure communication environment depends on both the platform and the way teams use it.
Small and midsize medical practices are bracing for the most significant overhaul of federal healthcare cybersecurity rules in more than two decades. Sweeping updates to the HIPAA Security Rule would eliminate the long-standing distinction between required and addressable safeguards, making every security control mandatory no matter a practice’s size or revenue. Key changes include mandatory multifactor authentication for system access, full encryption of electronic protected health information at rest and in transit, annual security risk assessments with specific structural requirements, regular vulnerability scanning, and detailed compliance documentation.
For a two-physician family practice or solo practitioner, these requirements mark a clear sea change because many organizations lack dedicated compliance or information security staff. The urgency stems from real-world risks: in 2024 alone, more than 276 million patient records were compromised in healthcare data breaches, with the average incident cost now running around $10 million. HHS enforcement data shows that over half of financial penalties in recent years targeted small medical practices, and agency statements make clear that practice size will no longer serve as a mitigating factor.
Industry groups have urged HHS to consider financial realities for under-resourced providers, yet the core trajectory remains focused on stronger risk analysis and management. Practices that begin planning now will be better positioned when the final rule takes effect, whether the timeline aligns with the May 2026 target or shifts later. Those that wait risk not only regulatory penalties but also the operational disruption of a single ransomware event.
Concrete steps available today include mapping how patient data flows through systems, enabling multifactor authentication with strong passwords, encrypting all devices that store or transmit information, training staff regularly through phishing simulations, segmenting networks, building and testing an incident response plan, vetting vendors through clear business associate agreements, and staying current on threat alerts. These measures directly support safer technology environments for every practice tool, including telephony solutions that handle scheduling calls, patient intake, and referral communications. By addressing these issues in advance, medical offices can protect sensitive patient information, maintain operational continuity, and demonstrate strong stewardship when evaluating or upgrading communication systems that touch protected health information every day. small practices face growing cybersecurity burden
Healthcare practices face mounting pressure to strengthen cybersecurity as federal rules tighten around electronic protected health information. A proposed overhaul of the HIPAA Security Rule eliminates the longstanding distinction between required and addressable safeguards, making every technical control mandatory regardless of practice size. This includes requirements for multifactor authentication on all systems accessing patient data, encryption of information both at rest and in transit, annual security risk analyses, vulnerability scanning, and detailed compliance documentation. For many small and midsize medical offices, these changes represent a significant operational shift rather than a simple compliance checkbox, especially when staff and IT resources are limited. Practices that have already conducted structured risk analyses, enabled MFA where possible, encrypted key systems, and reviewed vendor agreements through business associate agreements stand to gain a clear advantage.
The underlying focus on risk management and incident readiness aligns directly with everyday threats that phone systems encounter, such as unauthorized access to call logs, voicemail messages containing patient details, or recorded conversations. Modern telephony platforms must therefore support segmentation of clinical traffic, secure storage of recordings and transcripts, and audit-ready logs to meet these evolving standards without adding complexity to daily workflows. Practices that treat cybersecurity as an integrated part of technology planning rather than a separate IT project can reduce exposure during system evaluations, migrations, or upgrades. This proactive stance not only protects patient trust but also helps maintain smooth operations when phone systems become the primary channel for scheduling, referrals, and after-hours care. HIPAA Security Rule update
Frequently Asked Questions
What should a medical practice consider before updating its phone system?
Before updating a medical office phone system, practices should review call patterns, staff workflows, routing needs, and future communication requirements. A successful upgrade focuses on improving daily operations rather than simply replacing outdated hardware.
How can a medical office phone system upgrade support HIPAA compliance?
A medical office phone system upgrade can support HIPAA-compliant workflows by helping practices manage access controls, secure data handling, and vendor agreements. The technology should work alongside staff procedures and security practices to protect patient information.
What features should a medical office evaluate when replacing a phone system?
When replacing a medical office phone system, practices should evaluate call routing, voicemail management, after-hours communication, administration tools, and integration with existing workflows. Choosing a system that matches operational needs can improve efficiency and communication consistency.
Disclaimer: This article is for general informational purposes and is not legal advice. Practices should review communication, privacy, and compliance policies with their legal, compliance, or administrative teams.
Disclaimer: This article is for general informational purposes and is not legal advice. Practices should review communication, privacy, and compliance policies with their legal, compliance, or administrative teams.
You may also be interested in: The Role of IoT in Healthcare Communication
Missed calls, scattered text messages, and voicemails buried in separate apps can slow patient communication and add compliance risk. RingRx brings voice, secure texting, fax, video, and on-call communication into one HIPAA-compliant platform built for healthcare workflows. Start your RingRx free trial today.
Powered by flareAI.co